

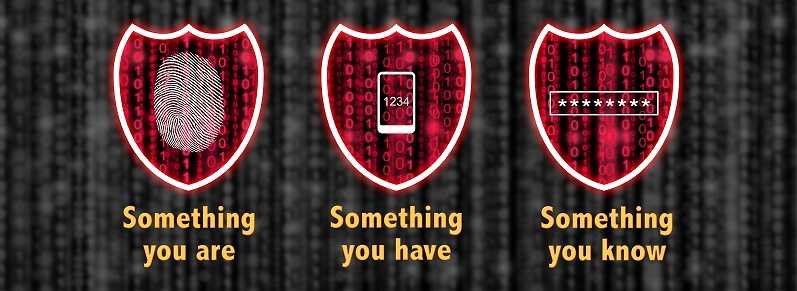
Here is a startling statistic: Within Facebook, Instagram, and Twitter combined, there are more than 80 million fake accounts. The majority of them, according to security company Easy Solutions, are there strictly to scam someone. As a result, any time multi-factor authentication (MFA) is offered, it’s a wise choice to take advantage. As an organization with mobile apps and access for customers online, it’s important to implement these features.
 Why is this? Because companies who have mobile apps and don’t add protection features such as MFA are four to nine times more likely to be affected by rogue applications. In addition, they are more prone to phishing attacks.
As an individual, go to the effort to use MFA when it’s offered, especially for financial accounts. This could mean ordering a fob from the institution, which will generate random numbers that are entered before access to the account is granted. It could also mean the organization will send a text message with a code that must be entered correctly before access is granted. There are other forms of MFA such as choosing a correct answer from a list of pre-determined questions. Whichever option may be provided, set it up for added security for your accounts.
 In addition, change passwords for your online accounts regularly. Quarterly is recommended, especially for financial accounts. Use at least eight characters that include upper and lower case letters, numbers, and special characters.
Organizations that host online accounts and apps should make it easy for customers, members, and clients to use MFA. By doing so, it will not only add the additional protection, but also will help to build trust. For financial companies, implementing biometrics is worth consideration.
Regardless of what MFA is chosen, anything is better than nothing.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




