

We all like to save money. However, most of us prefer not to do that at the expense of giving up our private information. Unfortunately, those who pinched the pennies and chose to use some low-budget smartphones are doing just that.
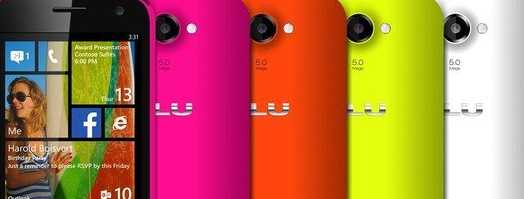
 Security researchers found that some BLU (Bold Like Us) phone devices were sold with pre-installed malware that sends contacts, messages, and location data from the device to China. The number of devices affected is around 120,000. The company is based in Florida, but manufacturing of the devices happens in China. The offending software is from a company called Shanghai ADUPS Technology Co., Ltd. The program, Adups, was loaded onto these smartphones in order to screen out junk text messages and calls from advertisers, the company claimed.
Anyone who has one of these devices is encouraged to apply the patch that Blu released to fix this backdoor issue immediately. The affected models are:
- R1HD
- Energy X Plus 2
- Studio Touch
- Advance 4.0 L2
- Neo XL
- Energy Diamond
These are sold at major retail outlets including Amazon and BestBuy.
BLU stated that the devices should have auto-updated, but if you aren’t sure, you can check in your settings. Go to Settings>Apps>Menu Icon>Show System>Wireless Update. This will let you know what version of the operating system is installed. If it’s between versions 5.0.x and 5.3.x, you need to update it.
If you’re not so worried about your data going to China, you still need to update your device. Researchers at Kryptowire said they were also able to execute remote commands with system privileges, as well as reprogram the device.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




