

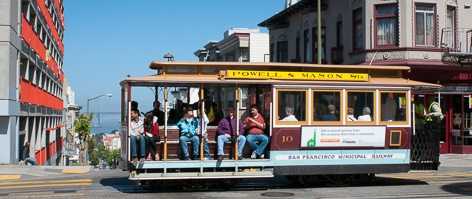
In San Francisco over the Thanksgiving weekend, anyone getting out and about using the Municipal Transportation Agency (nicknamed Muni) was rewarded with free public transportation for a couple of days. This was due to the Muni network being hit with ransomware.
According to a report by the San Francisco Examiner, over 2,000 Muni payment and scheduling systems were affected, causing officials to open up the fare gates so customers would not be impacted by the attack as they took advantage of Black Friday sales. The attacker asked for 100 bitcoins in exchange for the decryption key. That amount is worth roughly $73,000.
Fortunately, unlike some other hospitals and even police departments, Muni had recent backups and were able to restore. The recommendation for all organizations is to create regular backups of all of the important data so that if something like this does strike, it can be quickly brought back online and the cyber criminals don’t get a huge payday.
 It is not recommended that a ransom ever be paid. That just encourages this type of crime. Unfortunately, some companies have contributed to the success of ransomware by coughing up the money. Ransomware has been on the rise for the past several years. Earlier this year, the FBI issued an alert recommending that individuals and organizations take some actions to prevent paying:
- Prepare by implementing awareness training for all employees and prevent the attacks by adding access controls, updated anti-malware tools, and lock down admin-level accounts.
- Create a business continuity plan for dealing with these types of attacks, which should include regularly backing up data, verifying the backups, and making sure those backups are separate from the associated networks.
What “regular” means is dependent upon the type of business. For hospitals and other organizations that need more real-time data available at all times, it may mean anything from every 15 minutes to an hour. For others, it may mean nightly. However, it should be often enough that if the data does need to be restored, it’s as current as possible.
The perpetrator of this was someone going by the alias “Andy Saolis.” The ransomware was HDDCryptor, which not only affects PCs, but can also get to network-connected drives, servers, and other types of devices such as connected USB drives.
The gates were functioning normally by the Saturday after Thanksgiving and once again, payment is required to ride.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




