

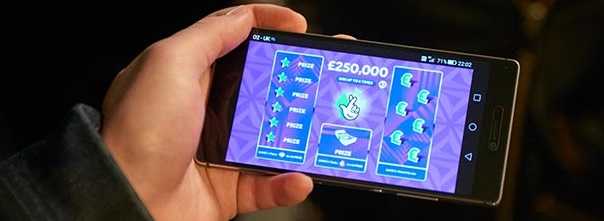
For those who like to play the lottery in the UK, it’s possible hackers have stolen your information. The UK National Lottery reported that roughly 26,500 players’ accounts were accessed and that email addresses and passwords were taken as a result. Being blamed for this is password reuse.
Password reuse is the scapegoat often these days. It has been blamed recently for intrusions into music streaming service Spotify and the massive breach of LinkedIn that resulted in the theft of data for over 167 million users. You should always use a different password for each online account. This is  especially important for any site that stores sensitive data such as financial information, social security numbers, or healthcare data. It should be second nature to create strong passwords by now. They should include the following:
- At least one special character, such as “#” or “@.”
- At least one number. More is better.
- At least eight characters.
Good passwords should not be:
- Familiar names and places.
- Dictionary words or phrases
Should not include:
- Sensitive information such as driver’s license numbers or social security numbers.
- Confidential information about you or anyone close to you such as birth dates of family members.
 One tip for creating a strong and unique password is to choose a base password of at least six characters. Then, use characters from the website you are logging into to finish that password. For example, CI5#$h could be your base and if you are visiting Amazon’s site, you could include an “A” and an “N” with that to be “CI5#$hAn.” It is highly unlikely you will ever duplicate that for another site. Just be sure to change your passwords regularly, such as quarterly if possible. The more often you change them, the less likely they will ever be re-used by someone with ill intent.
Officials for the UK National Lottery said they noticed some suspicious activity on some online accounts and that information from another website the players use was how the hackers got into these accounts.
Those affected will be required to change passwords. The company that organizes the National Lottery, Camelot, is also contacting players to help them change passwords if needed, and to offer security advice. Camelot does not believe that any of their databases were accessed in an unauthorized manner so draws or payment of any prizes should not be affected. They also do not store payment card or banking details and claim that no funds were either removed or deposited.
 While some security experts recommend using a password manager, others warn that it adds some risk higher than just creating your own unique passwords. For example, if the password manager site is breached, the hackers have your master password and therefore access to all of your passwords. So use caution when using these services and products. In fact, a security researcher proved that the password manager LastPass was vulnerable and how he was able to retrieve all the passwords stored there. So don’t believe that just because a site claims it is safe that it truly is. Just understand the risks of whatever method you use to remember your passwords, be it writing them down on sticky notes (not recommended) or writing them on a legal pad and locking them in a drawer (more reasonable).
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




