

The network security company, Watchguard released a report for the fourth quarter of 2016 and the findings were not pretty. It found that legacy security solutions are inadequate for detecting zero-day malware attacks. In fact, they fell short 30% of the time.
Also found was that old threats are new again. The cybercriminals are continually updating and modifying these threats to be new and improved. Macro-based malware is staying in the spotlight and the authors have even updated these to use the newest Microsoft document formats. Nation-state actors are using the old PHP shell attack tricks and JavaScript is still popular as a way to phish in email and over the Web.
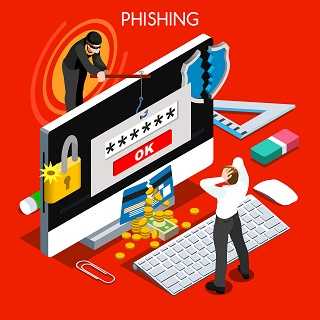 These are reminders that staying alert to what comes to our device screens is never old news. Phishing is continuing to be a thorn in our side and it’s necessary to always be certain that links and attachments are safe to open. This applies even if the sender’s name is someone we recognize. It’s very easy to spoof (fake) a sender’s name and make it appear to be someone familiar. However, if what is in the message is not expected and there is no explanation as to what it is and why you should trust it, just move it right to the trash. If you feel the need, verify it with the sender by picking up the phone, sending a text, or walking to his or her desk.
It is easy to forget, that clicking on links while perusing social media also presents significant risk of downloading malware or becoming a victim of a phishing attack. Use caution when clicking those as well. If you are not certain they are going to take you where you expect them to, just don’t do it.
The WatchGuard report also found that most network attacks target browsers and web servers. Of the top attacks, 73% were conducted using drive-by download attacks. This can happen when you merely visit a site that is running malicious code, even if just for a few seconds.
The top network attack affected Germany almost exclusively. The WScript.shell remote code execution attack caught out that country’s users in 99% of the recorded cases of this.
The WatchGuard Internet Security Report used anonymized data from more than 24,000 active WatchGuard appliances all across the globe. Unfortunately, a conclusion of this is that the cybercriminals are consistently staying one step ahead of anti-virus and anti-malware solutions. It’s up to the human eye to take up the slack and be another first line of defense against malware.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




