

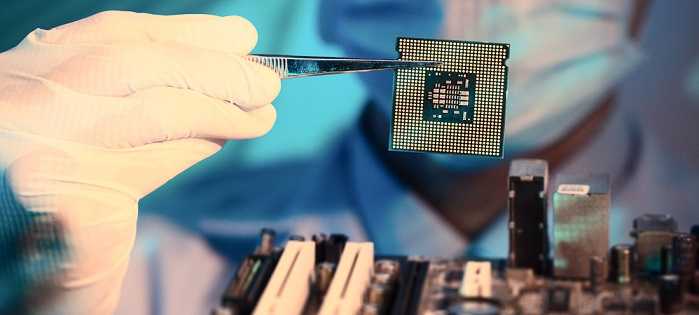
It really is possible in the cyber world to miss a critical vulnerability for a very long time; decades, in fact. It happened in 2015 with the discovery of the encryption-related FREAK vulnerability in browsers as well as with some outdated encryption the government mandated that created an issue referred to as “logjam.” In this recent discovery, it is an issue with Intel chips that could allow an attacker to gain complete control of a device, even when it’s shut down or sleeping and without having a correct password.
 Intel’s advisory labels this one (INTEL-SA-00075) “critical.” It affects desktop PCs, laptops, and servers dating back to 2010 and running on firmware between versions 6.0 and 11.6. It does not affect consumer-based PCs with consumer firmware. Intel has also provided a tool that will allow users to determine if their PCs are vulnerable.
Those affected should apply the patches as soon as they are released. Intel is working with its partners and some patches are expected to be available the week of May 8.
This vulnerability has been confirmed by two separate researchers: Embedi and Tenable. If it’s exploited, the attacker takes advantage of Intel’s Active Management Technology (AMT). AMT allows administrators to connect remotely to the PCs to perform maintenance on large groups of them at once. It can allow remote control of the keyboard and mouse even if the computer is turned off. Another feature of AMT functionality is that it allows access to a sleeping computer via the browser. A password must be entered by the admin to do this. However, the flaw will allow a hacker to enter a blank password and still access the web console to get to the device. Embedi warned that any affected internet-facing device with ports 16992 and 16993 open are also at risk.
It is either unknown, or undisclosed, how many devices this affects as of writing. However, a search on Shodan, a tool that allows users to find specific types of computers connected to the Internet found upward of 8,000 affected, with 3,000 of those in the U.S. alone.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




