

Police departments have long been victims of successful hacking efforts. Cybercriminals make their way into law enforcement systems and often hold data for ransom, demanding payment to restore critical information needed for daily operations. A recent attack on law enforcement took a new twist when the official Twitter account and website for London’s Metropolitan Police was hijacked. The disturbing, profanity-laced, and often nonsensical tweets were posted for about forty minutes before being discovered and then removed.
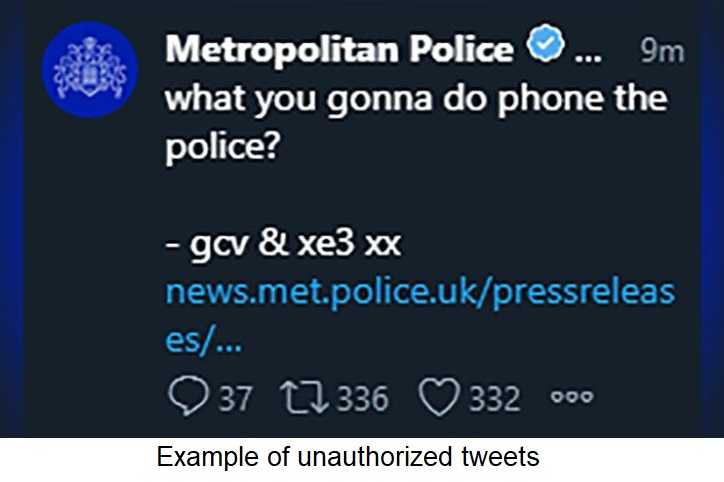 That was just one of the tweets posted on the Metro Police Twitter account. Metro Police services use an online service called “MyNewsDesk” to communicate with the public via tweets and press releases, as well as emails sent to subscribers. Currently, authorities believe the IT system itself appeared to be spared in the hack. The investigation is ongoing and no person or group has currently been found responsible. But what is being considered are the online security practices and systems data security used by Metro Police and the MyNewsDesk service. A closer look at security protocols are necessary to prevent further, and possibly worse, attacks.
While this one occurred on the other side of the pond, this hack was just one of many targeting organizations of all types. In 2017, both HBO and McDonalds had their Twitter feeds pirated by cybercriminals. Vulnerabilities such as weak passwords and lack of multi-factor authentication (MFA) can easily be the source for these and other hacks. It’s important to not only have strong passwords that include letters, numbers, and special characters, but also to use multi-factor authentication whenever it’s offered. Twitter does indeed offer that service, as does Facebook, Google, and many other online services.
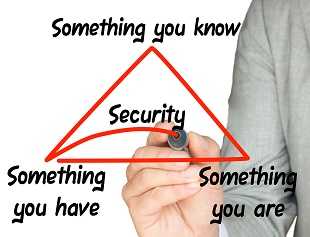 Although this particular incident was relatively harmless, organizations that don’t require additional security steps to verify a user leave themselves wide open to attack. MFA requires additional actions to authenticate a user is who they claim to be when logging in. If a password is hacked, the added layers of verification–often including an additional security code sent to the user’s phone–can stop a hacker from successfully logging in. Both individuals and organizations should always take advantage of MFA whenever it’s available for all their accounts, especially those dealing with sensitive information.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




