

It’s easy to become inundated with all the news about the novel coronavirus these days. It’s also becoming very easy to miss all of the other news that may still be important to know, even as we are all sheltering-in-place and avoiding social contact. In particular, Microsoft issued an advisory about a new zero-day vulnerability affecting all supported versions of the Windows operating system including Windows Server operating systems.
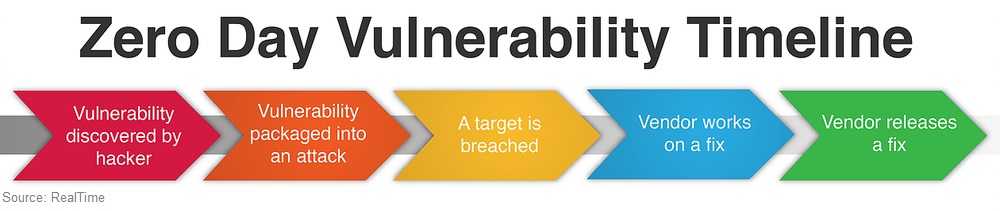
A zero-day vulnerability is one that is actively being exploited and for which a fix is not available. Though Microsoft is calling it critical, the company has no plans to issue an immediate fix. Instead, there have been hints that it will be in the next Patch Tuesday release in April. The reasoning is because attacks thus far have been targeted and limited, though as of writing, there is no indication of who or what companies may be the targets.
There are mitigation options in the meantime. Microsoft suggests the following:
- Disable the Preview Pane and Details Pane in Windows Explorer.
- Disable the WebClient service.
- Rename ATMFD.dll to something else.
 In addition, if you’re running a version of Windows that is no longer supported, consider upgrading it to one that is. In January, Microsoft stopped supporting Windows 7, so go to something newer than that. When a patch is available, jump right on it. Do not pass “Go” or collect $200. Just apply it. And remember to keep your cybersmarts on high alert and don't open attachments or click links in email messages unless you are 100% sure they are safe. Phishing is one way this zero-day attack has been successful.
This zero-day is located in the Adobe Type Manager Library (atmfd.dll) and there are two remote code execution attacks related to it. These could allow attackers to take over and perform actions on the device on the user’s behalf.
So, while you’re sifting through all the coronavirus news, don’t forget to keep your computers and devices wiped down and updated. Consider making the most of the updating time and sanitize it while it’s updating?
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




