

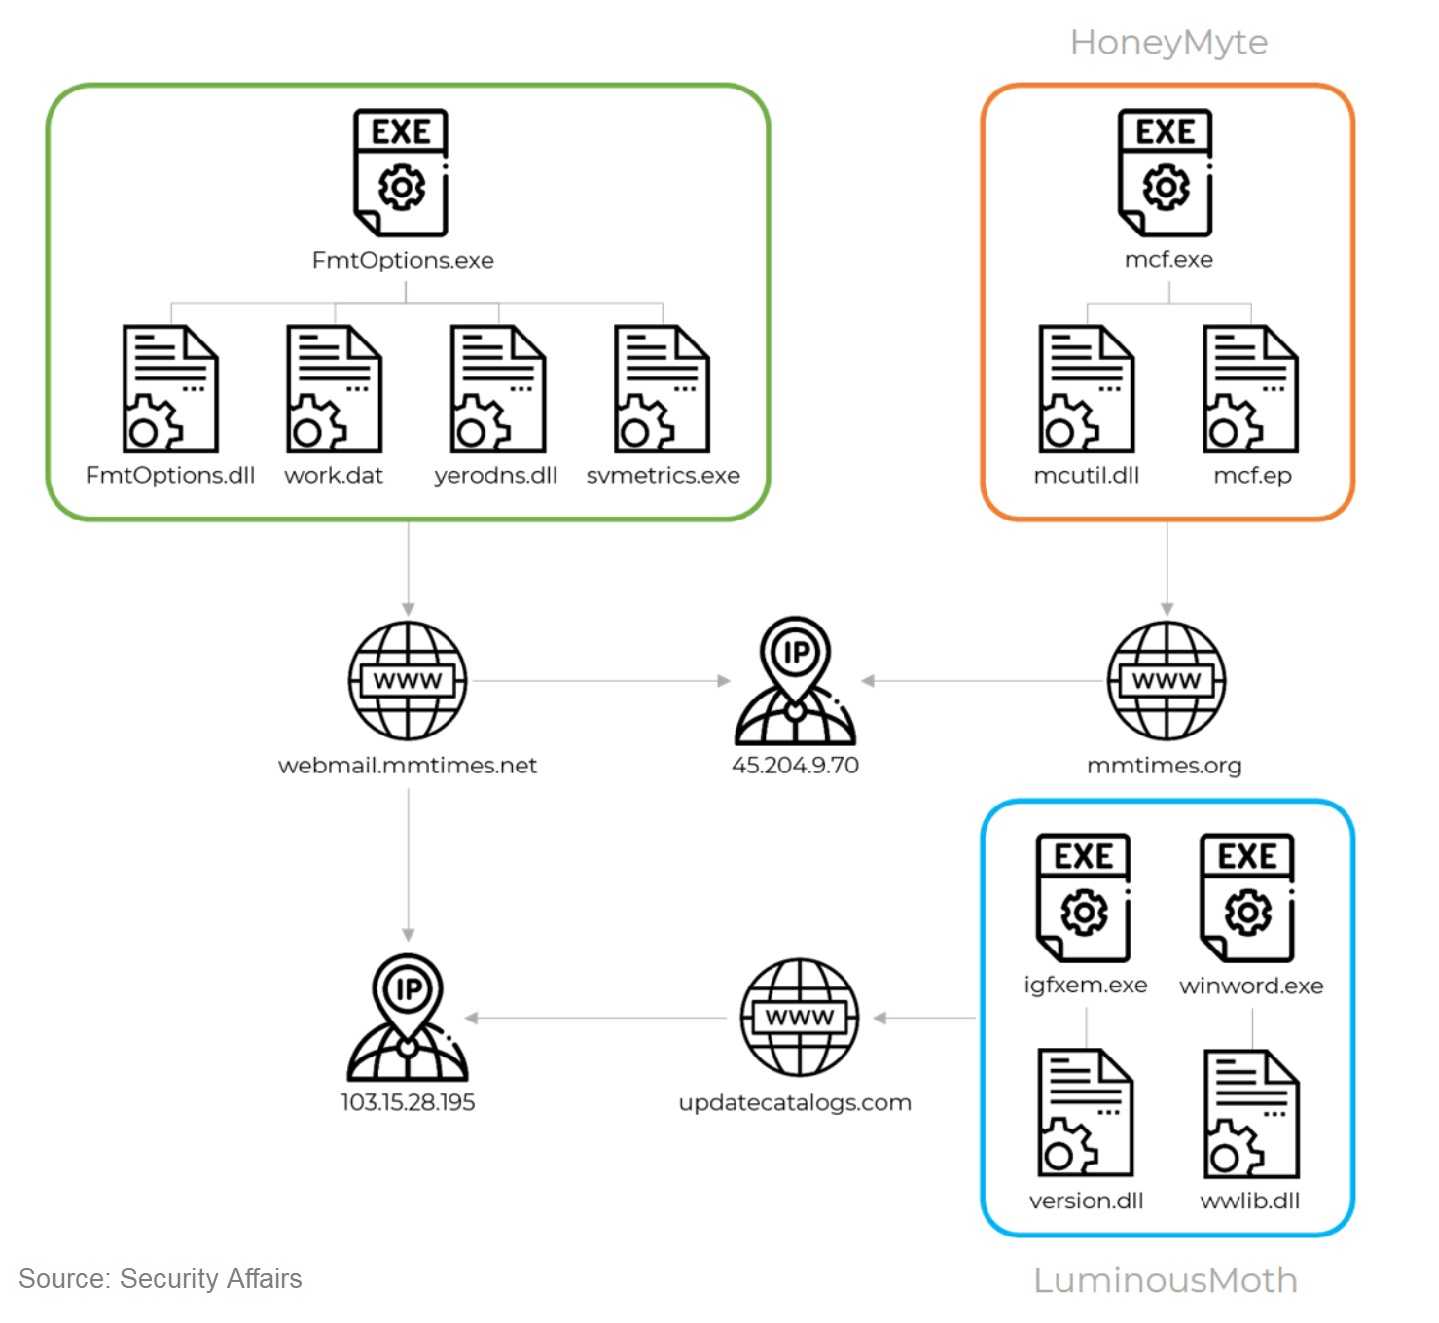
The conferencing app that catapulted into fame during the pandemic has become a tool for spying on governments in Southeast Asia. Kaspersky researchers dubbed the Chinese APT (advanced persistent threat group) LuminousMoth after they found the APT is pedaling fake Zoom software for their cyberespionage efforts. Doing so enabled spying on high-profile targets in Myanmar and the Philippines, with 100 and 1,400 victims respectively. Kaspersky finds these infection rates could be skewed, as they believe LuminousMoth was really after a small, select number of victims they could further exploit. The findings show the intended targets are government agencies in these countries and elsewhere abroad.
2
Spearphishing, which goes after individual targets by name, title, and other interests with alarming success, is the launching pad for this APT. This type of phishing email is typically after valuable information like business secrets and other confidential information. LuminousMoth sends spearphishing emails with infected links to download Dropbox, a cloud storage sharing service. Through a series of machinations, LuminousMoth deploys the fake Zoom app used to gather files they’re interested in, allowing for successful espionage on the intended targets.
The bogus Zoom software is signed by a Shanghai organization, and any files that could interest LuminousMoth are copied and sent to a command-and-control server (C2) for the group to dissect and gather intelligence on foreign governments. The group also searches for cookies and user credentials, including those involving Gmail accounts. They can then “hijack and impersonate the Gmail sessions of the targets” according to Kaspersky.
Since the pandemic exploded the need for video conferencing apps, countless organizations still depend on the Zoom app for daily interactions. LuminousMoth exploited the weakness behind the need and found Zoom software the perfect complement to their cyberespionage plans. With LuminousMoth casting a wide spearphishing net to start, they know their intended targets will likely be included in their web. What parts of the world will be included next is anyone’s guess.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.




