Bank of America advised customers that a vendor security breach compromised a blockbuster amount of PII. The stolen data was the result of a breach of one of the bank’s service providers, Infosys McCamish Systems (IMS). The vendor announced the breach, and by extension it led to the sensitive data of Bank of America customers being accessed. It’s estimated that more than 57,000 B of A customers were victims.
2
Breaches of third-party vendors are a growing security threat. A vendor compromise can lead to their own clients being breached. That's what happened with Bank of America. In this case, affected customers with deferred compensation plans were the victims. The exposed data includes first and last names, date of birth, physical address, business email address, Social Security number, credit card numbers, and other sensitive PII. As a result of the hack, Bank of America is offering those affected a free two-year membership in an identity theft protection service through Experian Identity Works.
2
Signing up for Bank of America's offer of identity theft protection service is always a smart move, including regularly monitoring your credit report for unusual activity. Remember, however, that this won’t prevent your credit being compromised. The monitoring service will give you a head’s up if something seems amiss.
Changing your account password with a minimum of eight characters that are a mix of upper-and lower-case letters, numbers, and symbols is strongly recommended after involvement in any security breach.
2
 The notorious Russian ransomware group LokBit claimed responsibility for the IMS attack. In a post on X by Dark Web Informer, the group claimed over 2,000 IMS systems were encrypted by its operators. LokBit offered the stolen data to the first bidder starting at $500,000.
LokBit's threat group was first discovered in 2019 and included their Ransomware-as-a-Service (RaaS) one year later. As an RaaS model, LokBit offers its ransomware to cybercrime groups worldwide for their own attacks, taking a percentage of the paid ransoms as their fee. LokBit is known for high-profile attacks and since 2020, there have been nearly 1,700 attacks in the U.S. costing a minimum of $91 million.
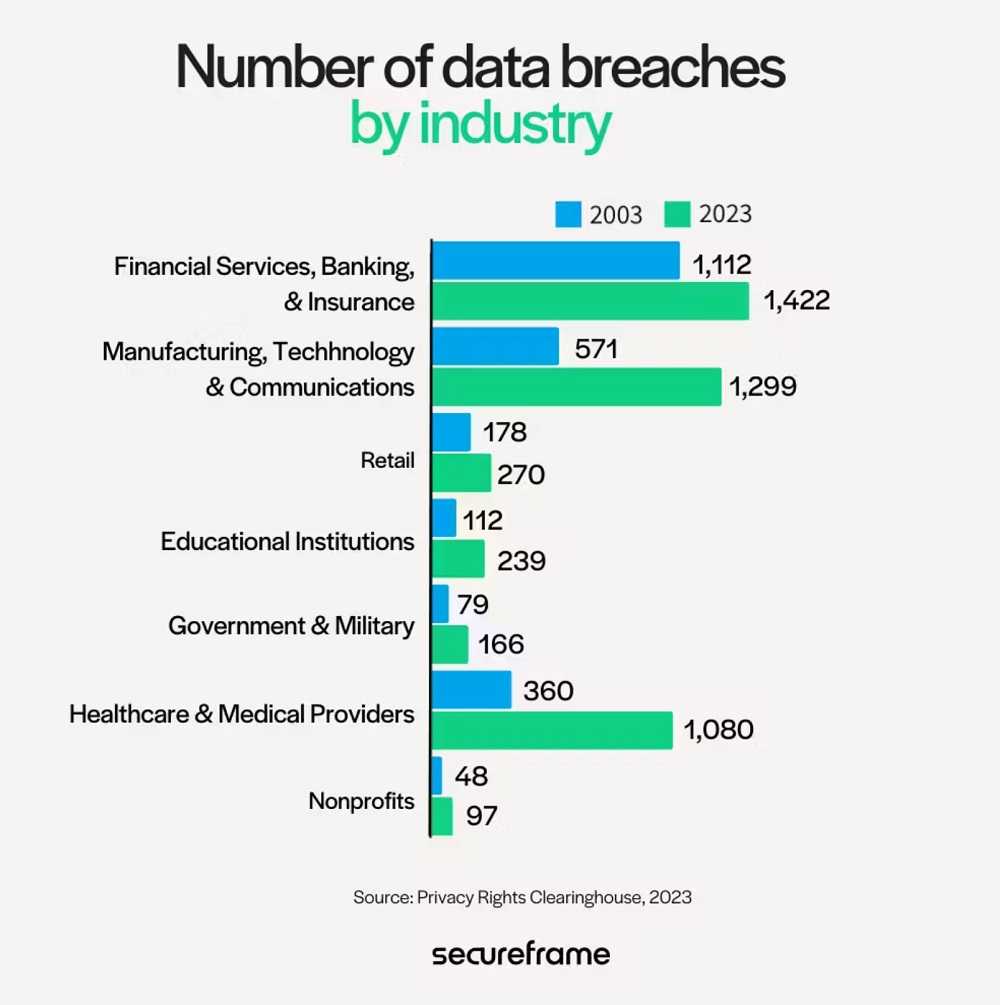
Bank of America is the second largest bank in the U.S. with total assets of $2.45 trillion and around 69 million customers in the U.S., making it a ripe target for cybercrime. And even though the bank wasn't directly hacked, the attack on IMS led to the involvement of the bank's customers.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.