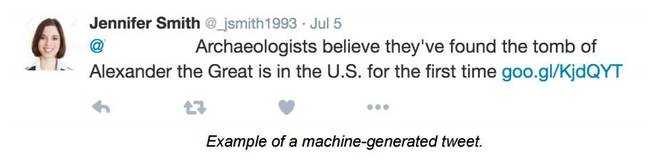
If phishing spam isn’t coming fast and furiously enough for you, some developers from security firm ZeroFox have created an automated spear phishing tool that snagged Twitter victims up to 60% of the time in testing. This is far more than the measly 15% that hooks “regular” Twitter phishing victims.
This tool uses learning technology. According to the creators, “The model is trained using spear phishing penetration data, and in order to make a click-through more likely, it is dynamically seeded with topics extracted from timeline posts of both the target and the users they retweet or follow.” The software then creates tweets that are relevant to those victims.
The basic lesson is never to click on links that you find anywhere in social media. This is especially true if you are not expecting them or don’t know the sender. Even if you do know the sender, verify the legitimacy of the link independently before taking action. In other words, don’t just click a link because you think your mom really did want you to “check this out!” If a link looks a bit strange or is shortened using one of the URL shortening tools, be suspicious. Those are used to intentionally to hide the address of malicious locations.
The testing for this new automated tool included over 2 million tweets and shows just how trusting people can be when messages are targeted to their interests. In this case, they focused on Twitter users who represented high value, such as those with a lot of followers or have a lot of retweets. This helped keep the phishing attack out of the line of site of the Twitter defenses. Fortunately, the creators of this tool are the good guys. However, it’s only a matter of time before the bad guys figure this out too.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.