Social Engineering is alive and well. It is used so often by cyber criminals because it works and often times, it's simple and even low tech. The old ways of getting information and stealing identities still work, such as pickpocketing, but the number one social engineering technique is still phishing email messages.
Following are some examples of ways information was acquired by the "good guys" to prove how simple it can be done and to make people aware, which really is most of the battle. All of the below tests were done ethically and the people or companies performing the tasks were either paid by the company to test their security or to prove a point and any physical items taken were returned.
 Let's start with the least technical, but still very effective pickpocketing. While you may immediately question if it's really social engineering, think about street performers, airport lines, concerts and other places where everyone is happy and distracted. Jim Stickley of Stickley on Security is infamous for robbing his friends. In one case, he was traveling with a colleague and noticed that the colleague carried his identification and credit cards in the back pocket of his backpack. When Jim questioned him, he said it was safer than having it separate when he travels. That is understandable as a wallet is one more thing to keep track of when travel gets so hectic. Well, when they were in line to check in, Jim unzipped the backpack and lifted his driver's license and credit cards, zipped up the pocket, and just kept talking.
When eventually they got to the check-in counter, he was called out and came clean, but he's really a novice and the professionals will use all kinds of ways to get that information including using magic tricks and children as decoys and distractions.
- Always keep those items close by and in front pockets whenever possible. While they can still be taken, it is more difficult.
- Don't carry credit cards you are not using. Most people use one card, but have many others in their wallets. If you don't need or use them, leave them in a secure place at home.
- Never carry your social security card with you. Lock it in a safe place at home.
- Always stay aware when in crowded places full of distractions and zip or button your pockets and purses. It just adds one more layer of complication for a pickpocket.
 Trustwave did their version of phishing to gain user login names and passwords. Nathan Drier and colleagues sent email messages to employees at a company pretending to be the IT department. The message explained that their external webmail server was upgraded and everyone needed to log in with their credentials. There was a link in the message that the employees clicked and therefore forfeited their user names, passwords, and in some cases their VPN access credentials. That kind of information can allow an attacker to get additional privileges on the network and do all kinds of damage.
- Don't fall for clicking a link or opening an attachment in email messages, regardless of who sends them and even if they're sent to your home address, unless you verify it separately first. If IT sends a message asking you to click something, make a call to the department or physically go check when possible, and verify that it's legitimate.
- If you have any suspicion of links or attachments in email messages, don't click them. Hackers can do damage to your home network or use your devices to perform malicious attacks against others.
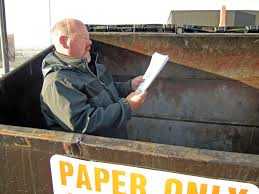 Dumpster diving is not social engineering in and of itself. However, a lot of information can be found in dumpsters that provide avenues into a company or someone's home or life. They are rarely locked and many companies or people don't bother to shred documents, even those that have confidential information. And once the trash bin goes onto the street, the contents are fair game.
- Stickley says that the lesson here is to shred everything. Even if you don't think it's important, it still might be to someone else.
- Invest a little more in a criss-cross shredder that also shreds credit cards and CDs. Even though CDs aren't used so much anymore, they are still often found lingering in files when it's time for spring cleaning. So, better to have the capability to shred them when it's needed.
Nathan Drier of Trustwave was once able to convince an employee that the workstation he was occupying and installing a backdoor onto was being fixed by him. And by picking up the phone and making a couple of calls, Stickley once convinced an employee to give him her password by pretending to be from the IT group of a company. This ultimately gave him VPN access directly into the company's network.
- Don't leave workstations unlocked when you get up to leave. Not only does that allow your co-workers to send embarrassing emails from your account, but it leaves a gaping hole in the security of the organization for people like Drier and Stickley.
- Never give passwords to anyone, in person or via phone. Even if you think the "IT guy" can get it anyway so what's the problem, don't give it to him.
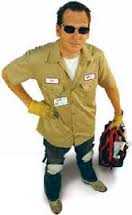 Stickley is quite the actor and has often convinced people he's an electrician, from a pest control company, an OSHA inspector, or even a flower delivery person in order to get past the front desk and roam around a company. Being any number of service providers, cyber criminals can do many things. This isn't just at the office, but also at home. A common scam in neighborhoods is for someone pretending to be an alarm company, knocking on the door and asking all kinds of questions about the security of the home in order to provide a quote. With all the wireless home security systems these days, any information about that can open all kinds of doors.
- At home, never give information to someone going door to door. If you are truly interested in the service, contact the company separately and not using information provided by the door to door sales rep.
- Always ask for credentials from door-to-door reps. Most locales require them to get permits and show them to you whenever they solicit business at homes.
- Ask questions of anyone that looks unfamiliar to you if you suspect they don't belong in the neighborhood or at the office. The more questions you ask, the less likely they will stick around to do harm.
- Don't trust someone claiming to be the IT guys or tech support if he or she asks for your passwords. They don't need you to give them to them.
The best defense against social engineering tactics is education, whether it's your family or your employees. And don't forget to have the conversations with the kids. With all the internet-connected devices they use now, they are not only a link in the chain, but a very important one.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.