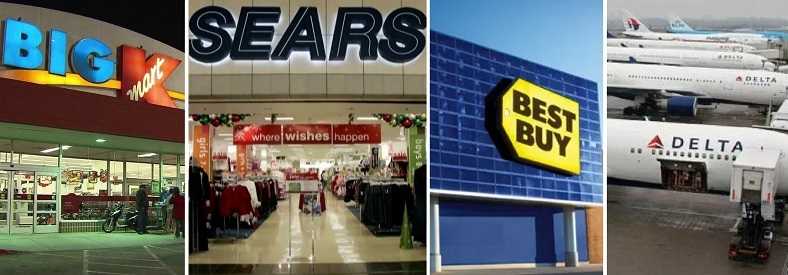
It’s getting to be old hat. Delta Airlines, Sears, Kmart and Best Buy customers have joined millions of others as victims of recent data breaches. The companies announced that a contractor notified them that information of “several hundred thousand customers” was potentially exposed during a breach that occurred between September 26 and October 12, 2017. The third party, [24]7.ai said that the names, addresses, payment card information including the CVV numbers and expiration dates of Delta customers is at risk.
 Delta cannot yet confirm how many customers were actually involved, but those who manually entered payment card data online to complete a transaction were most at risk. Those who used Delta Wallet were not included. Sears believes that less than 100,000 customers were impacted, although notes that Sears-branded cardholders are not included. Company spokespeople cannot confirm what information was compromised; only that passports and government IDs were not.
Again, it’s important to review payment card charges frequently these days. No longer is it sufficient to wait till the monthly statement is sent. If anything looks amiss, contact the card issuer immediately to get it resolved.
 In this case, it wasn’t the effected companies' systems' that was accessed. Delta hired [24]7 to conduct chat conversations on its behalf. This emphasizes how important it is for companies to ensure that the organizations with which they do business are taking care of their data. It’s OK to ask (and you should ask) them a lot of questions about their security processes and procedures, what security products they have installed and kept active, how often they update and patch systems, and about their mitigation plans should a breach occur.
Sears and Kmart will start a hotline to help customers wade through this and Delta has a page up on its website at delta.com/response. Best Buy is working to discover what data was exposed before they announce their plan of action.
Delta, Sears, Kmart and Best Buy join an ever-growing list of larger organizations that have had breach incidents recently. Others include Hudson Bay (Saks and Lord & Taylor), Boeing, Panera Bread, and UnderArmour when it’s MyFitnessPal site was accessed and 150 million health-conscious users were victimized.
For banks and credit unions
Share this article with your members
Copy a ready-made summary and link for your newsletter, website or social posts.